Security teams face mounting pressure to secure more applications, identities, and infrastructure across increasingly diverse environments. Yet many organizations continue to struggle with operational complexity, fragmented tooling, and inconsistent security practices that slow adoption and create management overhead.
Vault 2.2 introduces enhancements that make Vault easier to adopt, simpler to operate, and more scalable across enterprise environments. From onboarding and usability improvements within Vault to expanded automation and deeper IBM ecosystem support, these capabilities help organizations accelerate adoption while standardizing security across hybrid infrastructure.
»Accelerate time-to-value with a better Vault experience
Successful security platforms are not only powerful, but they must also be approachable for administrators, platform engineers, and application teams who interact with them every day. As Vault deployments expand across organizations, reducing friction becomes essential to broader adoption. In Vault 2.2, in-product adoption and onboarding features become generally available to improve the overall Vault user experience.
»Reduce risk and disruption with the Upgrade Analyzer
Organizations that stay current on software releases can adopt innovations faster, standardize operations more effectively, and respond more quickly to evolving business and security requirements. Up to date platforms mean teams can readily access and benefit from ongoing product enhancements, fixes, and security patches. However, deploying platform or product upgrades can be challenging while trying to maintain high standards of day-to-day operations, especially when they are perceived to be disruptive to business as usual. To help teams operate Vault more easily, Vault 2.2 introduces the Upgrade Analyzer, a tool built to provide transparency around upgrades. It supports Vault operators in planning which release to target and how to account for recommended prerequisites and known issues. The goal is to reduce the number of post-upgrade risks and make teams feel more secure in the Vault upgrade process by providing in-product information.
»Delight users with a more personalized Vault experience
Security practitioners spend long hours working within the tools that protect their organization. Small usability improvements can have an outsized impact on productivity, satisfaction, and long-term adoption. That's why Vault 2.2 introduces a series of user experience enhancements designed to make everyday interactions with Vault more intuitive, informative, and enjoyable.
Feature Spotlight cards on the Vault home dashboard help users quickly discover recently released capabilities and product updates without leaving the platform. These cards make it easy to understand the newly available features and enable customers to take full advantage of the upgrade, by making these announcements easily viewable within the product. By surfacing relevant innovations directly within the UI, teams can more easily stay informed and take advantage of new functionality as it becomes available.
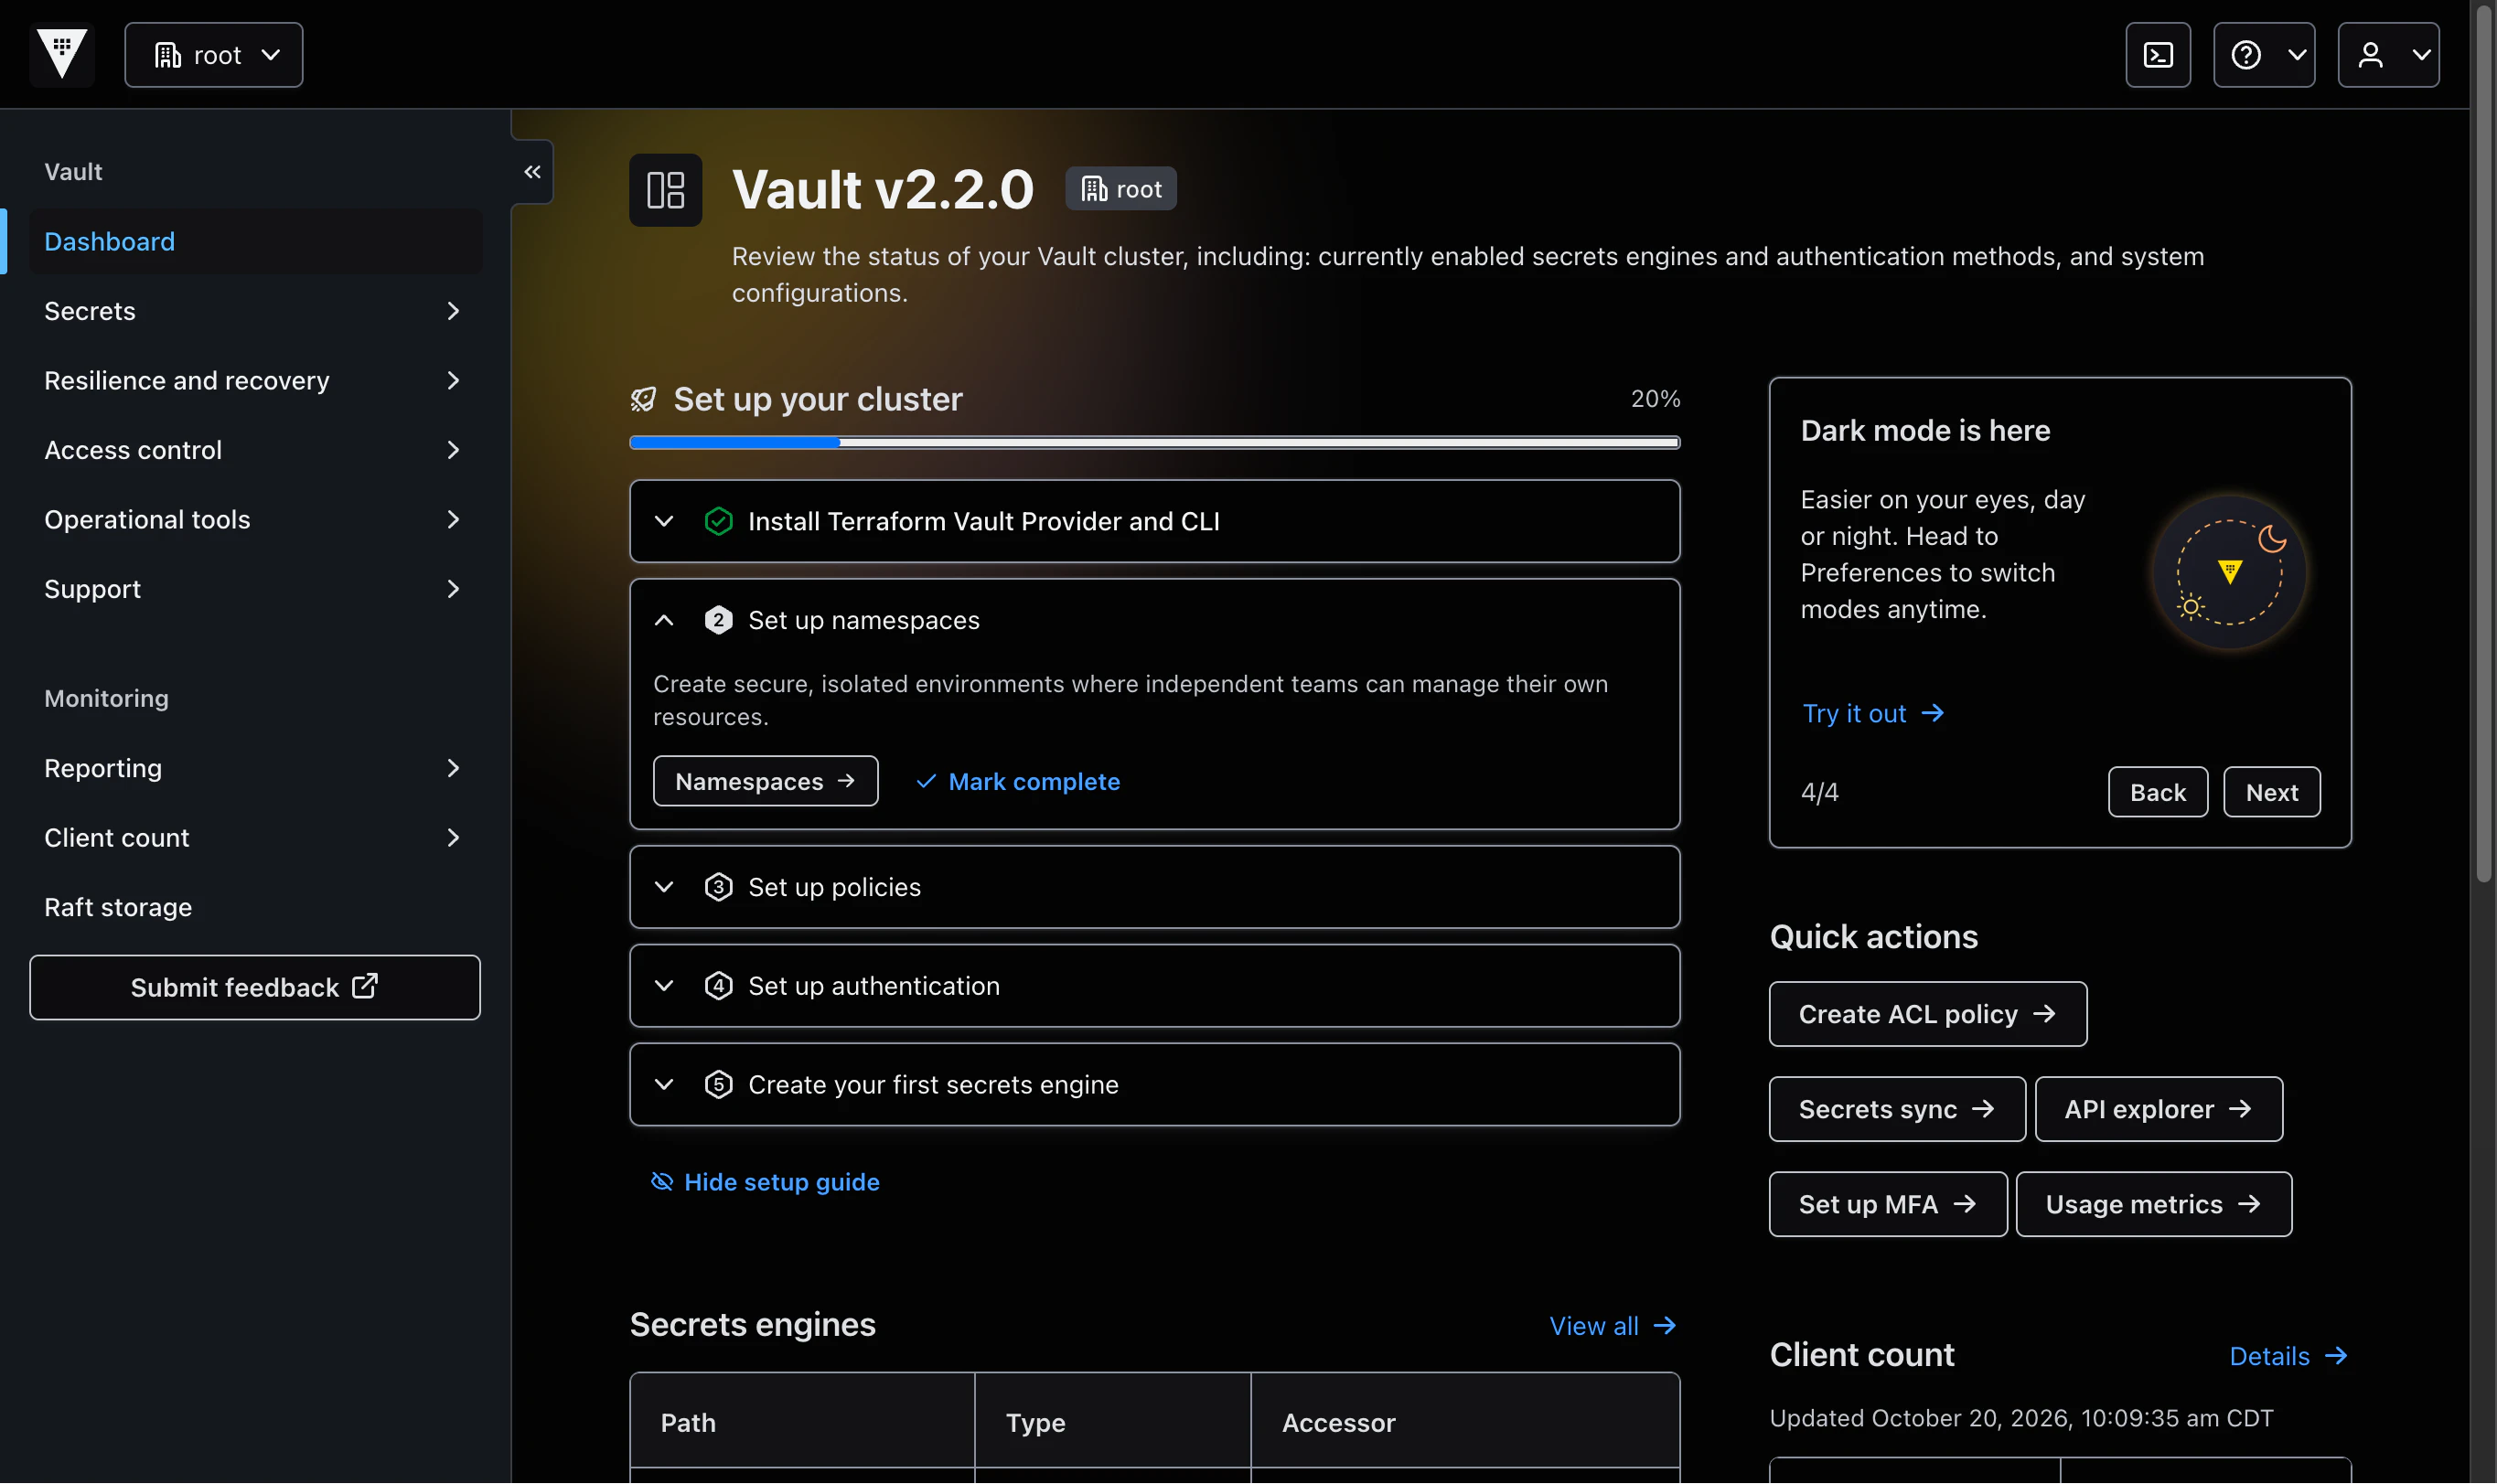
Updates to the Vault UI include enhancements to the home dashboard, dark mode and feature spotlights. Send feedback about valued features and suggested improvements from within the product with the Submit feedback button.
Dark mode has been a top ask from users. Vault delivers it with support from preferences, but it will default to the system values upon release. Preferences give individuals greater control over how they interact with the product. In 2.2.0, Preferences will support dark mode, in-product personas, and opting in to UI analytics.
»Submit feedback right from Vault
A new Submit Feedback button enables Vault users to provide input from the UI. We are grateful for and welcome feedback on how to improve features, other features that would be beneficial, or comments on what improvements you find most valuable.
As an example, Vault users could provide feedback on other features that might benefit from the customizability of preferences. While this button creates a venue for in-product contact, it’s also intended to enhance engagement with account teams or support. The feedback provided via the button will be monitored by the Vault Product Management team and contributes to the data that influence roadmap decisions.
»Reduce operational complexity through security automation
As organizations scale, manual security processes quickly become unsustainable. Managing secrets, credentials, and service accounts across multiple environments can create significant operational overhead and increase the risk of human error.
Vault 2.2 expands automation across credential and secret lifecycle management to help teams implement consistent security practices with less manual effort.
Vault 2.2 strengthens Azure Secrets Engine with automated rotation and immediately consistent Azure access tokens to resolve eventual consistency delay and reduce credential delays and drift. For LDAP Secrets Engine, account unlocking improves credential management within Vault and not in the configured external system, while proactive configuration validation with the LDAP Health Check identifies connectivity issues before failures occur, improving operational resilience.
Secret Recovery for KV v2 provides a safeguard against accidental secret deletion, helping teams recover critical information when mistakes occur. Usage Attribution offers deeper visibility into Vault consumption patterns, enabling administrators to better understand adoption, governance, and utilization across teams and environments.
By automating repetitive security tasks and improving operational visibility, organizations can reduce complexity, strengthen governance, and scale security programs more effectively.
»Extend consistent security controls across IBM and hybrid infrastructure
Enterprise infrastructure continues to evolve beyond a single platform or cloud provider. Many organizations operate a mix of IBM Power systems, Kubernetes environments, public clouds, and traditional datacenters. Securing these disparate environments often requires multiple tools and inconsistent operational processes that increase complexity and slow adoption.
Vault 2.2 helps organizations establish a consistent approach to secrets and identity security across their infrastructure footprint.
The Vault Client on IBM Power, now available in beta, enables teams running mission-critical workloads on IBM Power to leverage the same Vault workflows and operational model used elsewhere in the enterprise. This is planned to be made generally available in a follow-up patch release this year. Vault Secrets Operator (VSO) on IBM Power extends Kubernetes-native secrets and certificate management capabilities to IBM Power environments, helping platform teams standardize security practices across both modern and traditional infrastructure.
Vault 2.2 further strengthens cloud-native integrations with support for Azure AKS Workload Identity, enabling secure workload authentication without relying on long-lived credentials. This helps organizations simplify identity management while improving security across Kubernetes deployments.
Secrets Sync with Vault’s DB secrets engine enables organizations to maintain control over secrets, while making them available through external secrets stores, including cloud service providers and other destinations. Vault 2.2 now sources secrets from Vault’s database secrets engines, including instant updates for rotating database secrets, and enables encryption of those secrets in AWS and GCP. With these updates, rotating secrets across a distributed hybrid deployment is a simple API call.
These capabilities allow organizations to extend consistent security controls across diverse environments, helping reduce operational silos while simplifying security management across hybrid infrastructure.
»Standardize security and scale with confidence
As organizations expand across cloud, on-premises, and IBM environments, security success increasingly depends on the ability to simplify operations while maintaining consistent controls.
Vault 2.2 delivers improvements that help organizations achieve both. Enhanced onboarding and usability features accelerate adoption, expanded automation reduces operational overhead, and deeper IBM and hybrid cloud integrations help standardize security practices across the enterprise.
The result is a platform that enables organizations to reduce complexity, eliminate tool fragmentation, and scale modern security practices wherever applications and workloads run.
»Drive adoption and simplify Vault operations
Vault 2.2 delivers new capabilities that make Vault easier to adopt, simpler to operate, and more consistent across hybrid environments. To take advantage of these enhancements, we encourage existing customers to upgrade to the latest version and begin benefiting from the latest usability improvements, automation capabilities, and platform integrations.
Before the next GA, use the Upgrade Analyzer to assess your environment, identify potential upgrade blockers early, and plan your migration with greater confidence. By proactively evaluating your environment, you can reduce risk, minimize disruption, and accelerate access to the latest Vault innovations.